
Consulting/ Privacy
Consulting · Privacy
Records and Information
Management Privacy Evaluations
Which privacy regulations touch which of your activities — and what to do about it. Our team specializes in GDPR, CCPA/CPRA, and the growing patchwork beyond, with a proactive plan to get compliant and stay that way.
Privacy services
Our consulting team offers several privacy-related services to determine how your organization may be impacted by various privacy regulations, or to assist with a variety of other privacy-related initiatives. Four engagements, and most programs need more than one; they share a premise: privacy obligations land on the retention schedule, so that is where we fix them.
Records management evaluation
Ensuring your organization is compliant with different privacy regulations around the globe is a significant undertaking that requires time and resources. We help determine which of your organization's activities are affected by which regulations and create a proactive plan for you to be compliant — and stay that way. Regulations we specialize in: the General Data Protection Regulation (GDPR), the California Consumer Privacy Act (CCPA), the California Privacy Rights Act (CPRA), and more.
Proactive, not reactive — the plan is built before a request or an audit forces the question.
Retention period minimization
Propose opportunities and collaborate with stakeholders to defensibly decrease retention schedule periods, shrinking costs and risks associated with over-retention of records and personal information. We propose the reductions, then work them through the stakeholders who have to live with them.
Over-retention is the quiet liability: every extra year is more to store, more to search in discovery, and more to lose in a breach.
Privacy compliance monitoring
Receive updates on privacy laws and regulations to support ongoing compliance and make informed changes impacting your retention schedule — translated into the specific changes required, not a newsletter you have to interpret yourself.
Privacy law changes faster than any schedule refresh cycle. Monitoring is what keeps the two from drifting apart.
Compelled privacy review
Comply with mandatory privacy laws with defined maximum retention periods for regulated categories of personal data. Some laws do not merely permit deletion — they compel it once the purpose is served.
This is where privacy and recordkeeping genuinely conflict: one rule says keep it, another says destroy it. The schedule has to resolve both.
How an evaluation works
An evaluation is a scoping exercise before it is a compliance exercise. You cannot apply a privacy law to data you have not located, and most organizations hold more personal information, in more systems, than their own inventory shows.
Find the personal data
Identify what personal information you collect, where it lives, who touches it, and why you hold it. Purpose is the hinge — nearly every privacy regime measures how long you may keep data against the reason you collected it.
Match it to the law
Determine which regimes reach which activities. Jurisdiction rarely follows your org chart: it follows where your customers, employees, and processing sit, so one system can answer to several laws at once.
Put it in the schedule
Translate the findings into retention periods, disposition rules, and the documented basis for each. A privacy obligation that never reaches the retention schedule is an opinion, not a control.
The regimes we work in
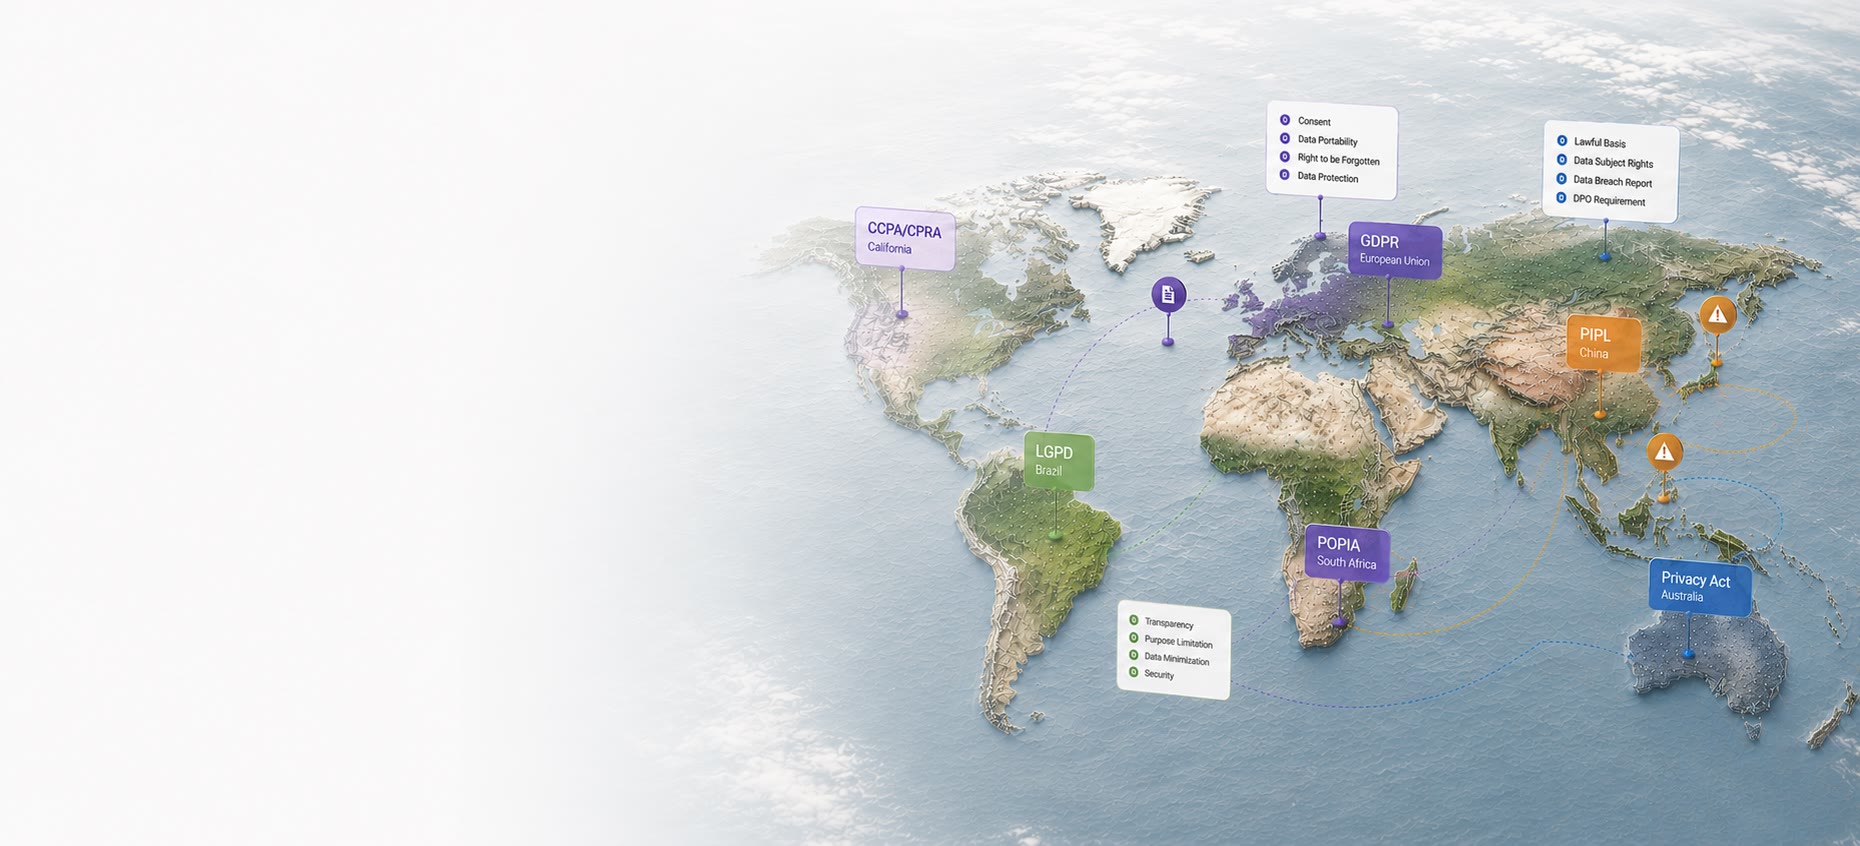
Our consultants specialize in GDPR and CCPA/CPRA, and work across the wider patchwork. What follows is what each one tends to drive in a retention schedule.
GDPR — European Union
Storage limitation is a principle, not a guideline: personal data may be kept only as long as the stated purpose requires. Drives documented lawful basis, data subject rights, and breach reporting into the schedule.
CCPA / CPRA — California
CPRA added an explicit retention angle: you must disclose how long you keep each category of personal information, or the criteria you use to decide. That is a schedule question before it is a privacy-notice question.
LGPD — Brazil
Closely modeled on GDPR, with its own regulator and its own legal bases for processing. Organizations with Brazilian operations or customers frequently discover it after building a GDPR program.
POPIA — South Africa
Conditions for lawful processing, with retention tied to the purpose for which the record was collected. Records kept beyond that purpose need a specific justification to stay.
PIPL — China
Separate consent for sensitive personal information and real constraints on moving data out of the country. Cross-border transfer is usually the requirement that reshapes an existing program the most.
Privacy Act — Australia
The Australian Privacy Principles require destroying or de-identifying personal information once it is no longer needed for a permitted purpose — an affirmative disposal obligation, not merely permission to delete.
What you get
Deliverables you can hand to counsel, IT, and an auditor. Not a slide deck.
Applicability findings
Which regimes reach which of your activities, and the reasoning behind each call.
Retention recommendations
Proposed periods for each affected category, with the legal basis documented.
Gap analysis
Where current practice diverges from the obligations, ranked by exposure.
A plan you can execute
Sequenced next steps, scoped to what your team can realistically absorb.
Who does this work
Privacy law, read by people who practice it.
Our privacy work is led by licensed attorneys who also hold privacy credentials — CIPP/US, CIPP/E, CIPM, and AIGP — alongside the records credentials the retention side demands. That combination is the point: privacy obligations only become real when they reach the schedule.
Meet the consultants →